Folders and visibility
Create a folder, set who sees it and who may file in it, and structure it with subfolders.
A folder is the unit in which access applies. Everything inside it – including every subfolder – is visible to the same roles.
Creating a folder
Open File storage and tap New folder.
Give it a name that someone will still understand in five years: "Accounting receipts" beats "New 2".
Write in the description what it is for. Everyone who sees the folder reads this later.
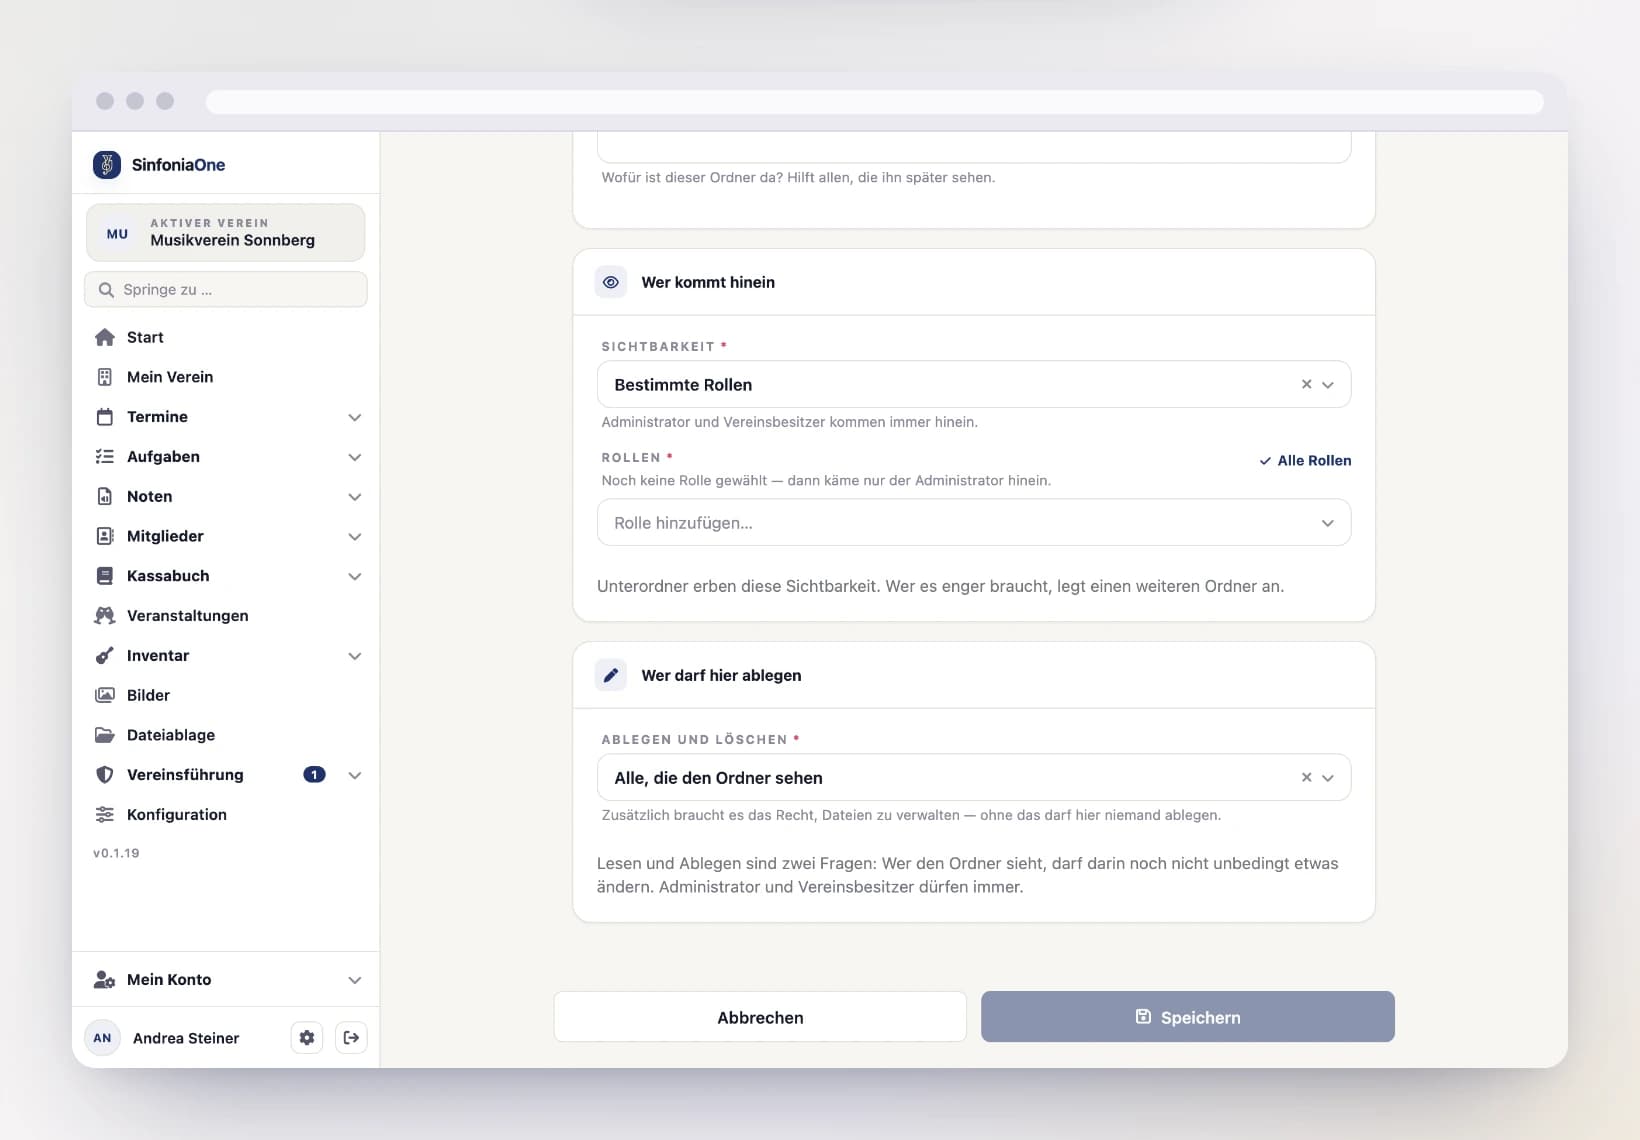
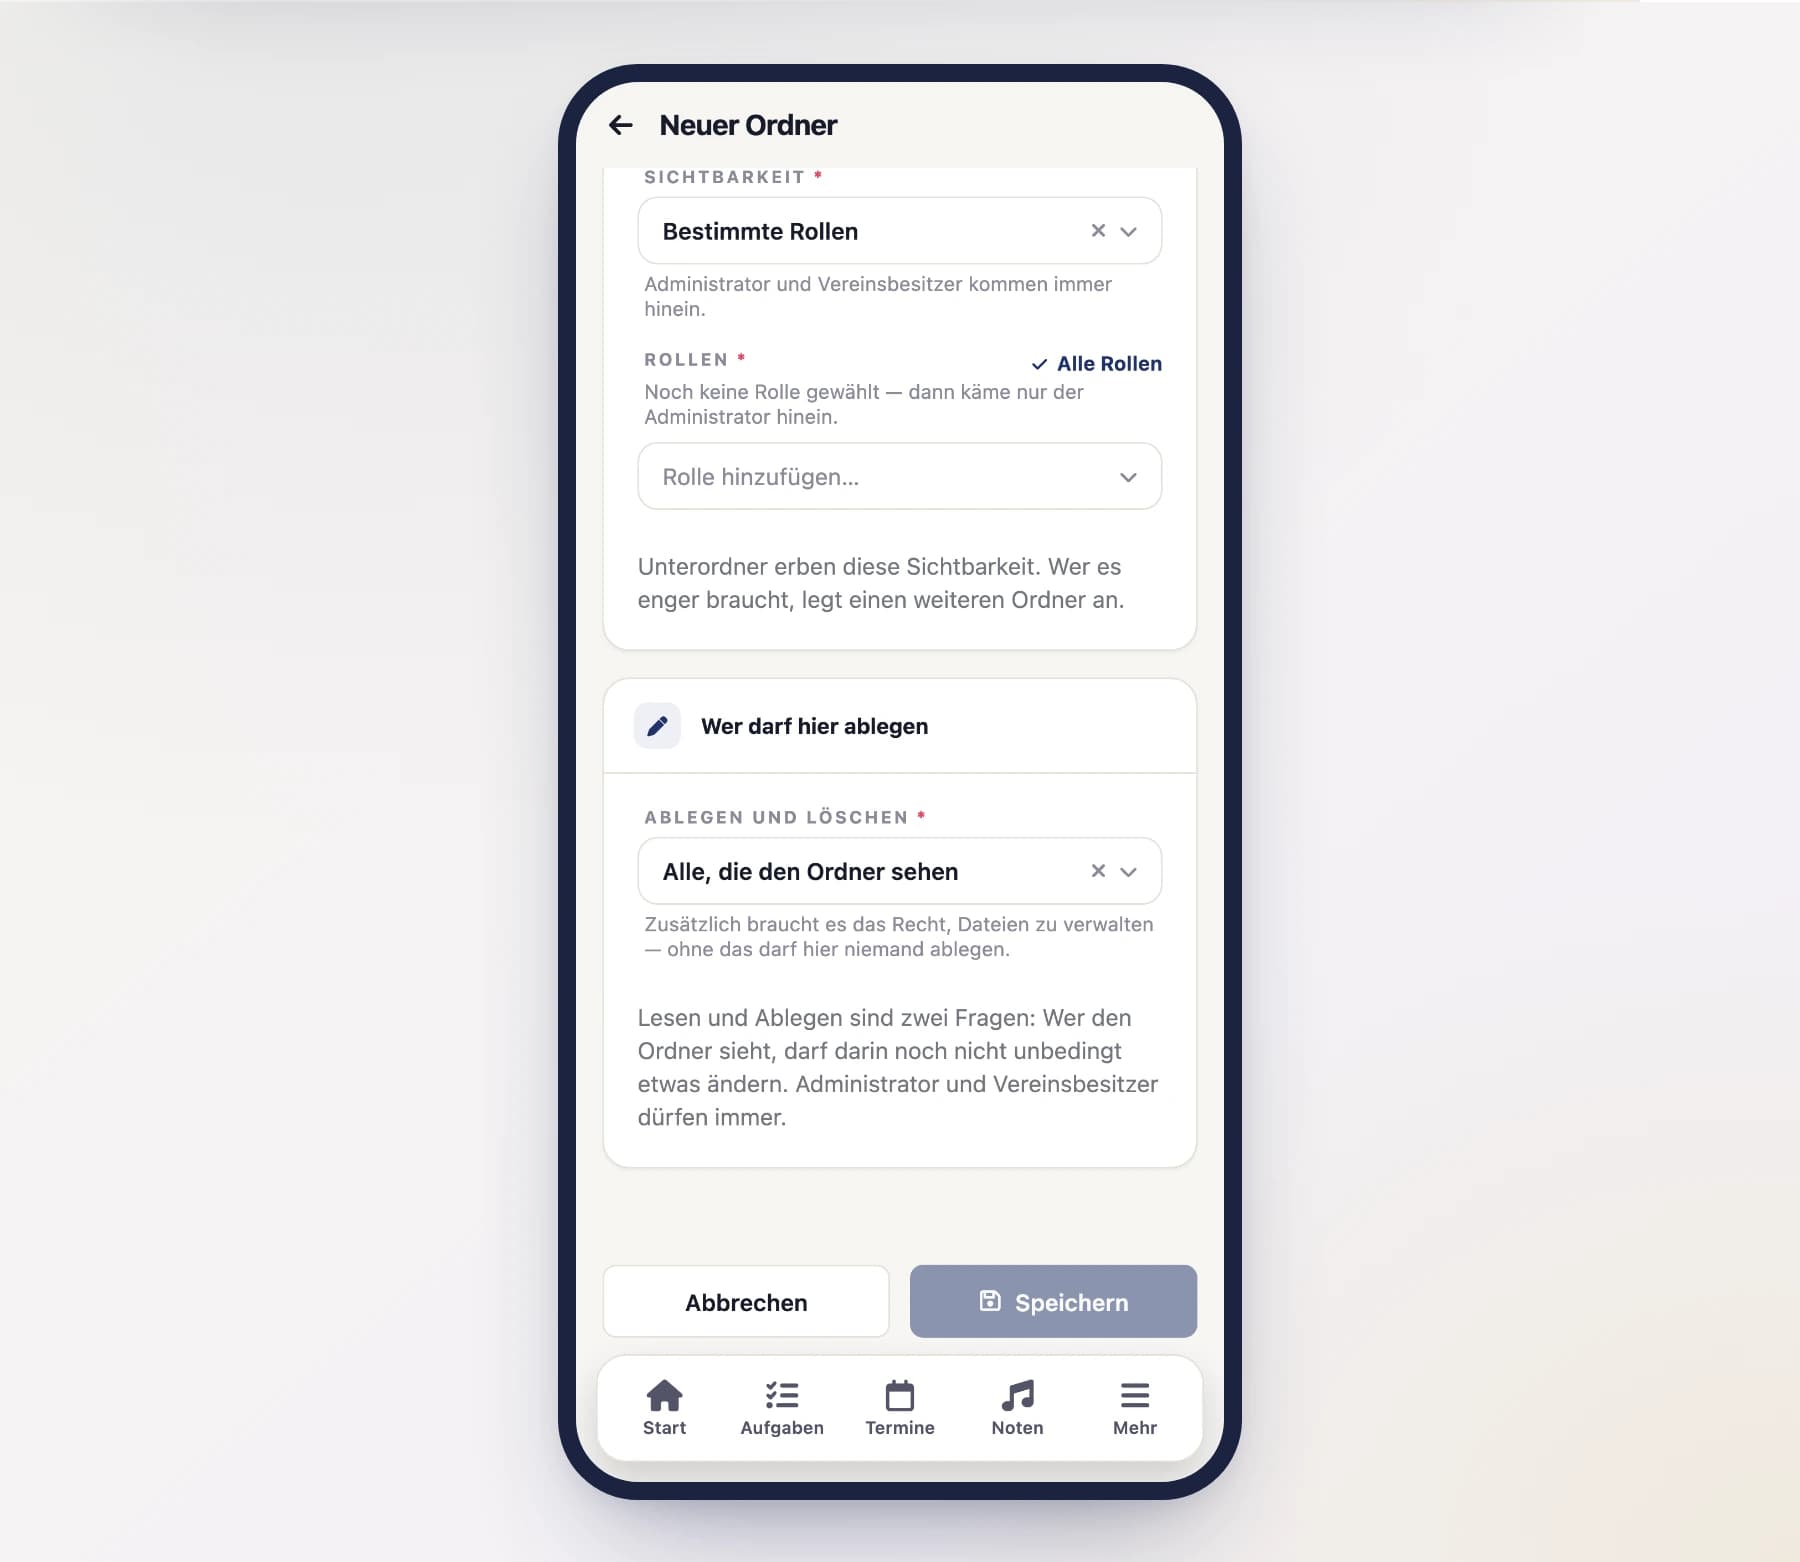
Choose the visibility: "Everyone in the club" or "Specific roles". For roles, tick who may enter.
Under Who may file here, decide whether everyone who sees the folder may put files into it, or only certain roles among them.
The path in storage stays
A path is created from the name when the folder is created. If you rename the folder later, only the display changes – the path stays. That is on purpose: mounted network drives will depend on it, and a rename must not tear them apart.
Changing the visibility later
You can open a folder up or narrow it down at any time. When you switch, the app asks precisely:
- From "Specific roles" to "Everyone in the club" – the role selection is cleared. Otherwise it would stay behind invisibly and suddenly apply again when you switch back.
- To "Specific roles" – you then have to pick at least one role. A folder without a role would be for the administrator only, and that is rarely what people mean.
Who may file
Seeing and filing are two different questions. The treasurer should see the receipts and put them there; the whole orchestra should see the statutes but change nothing.
That is why a folder carries a second line: Who may file here.
- Everyone who sees the folder – the default. Every folder you created before this distinction behaves this way.
- Specific roles – then only those may file, delete and create subfolders. The others still see the folder.
The permission remains the gate
Anyone without the permission to manage files may file nowhere – even if their role is listed here. This choice can only narrow, never unlock. Administrators and the club owner may always file; otherwise a club could lock itself out of its own records.
Only roles that can see the folder are offered. Take the visibility away from a role and it loses filing along with it.
Structuring with subfolders
Inside a folder you can create subfolders, "2025" and "2026" for example. You create them via New subfolder; the breadcrumbs above the list take you back out.
Subfolders cannot be narrowed
This is not a missing feature but a property of the storage system: anyone allowed to list a folder also learns the names of all subfolders – even of those whose contents would be denied to them. And a name like "Termination Müller" often gives everything away already. If you need a real boundary, use another top-level folder.
Deleting a folder
A folder can only be deleted when it is empty. Clear it out first. The reason: its files would otherwise stay in storage, be reachable through no view at all – and keep counting towards your allowance.
A deleted folder stays in the club's trash for 30 days and can be restored from there – with its name, visibility and roles.